Running the business
Website Compliance in Germany: Impressum, Privacy, Cookies and Accessibility
What should German businesses review on their websites? A practical overview of provider information, GDPR transparency, cookies, third-party embeds and the BFSG.
by Nguyen VoPublished on 8 min read
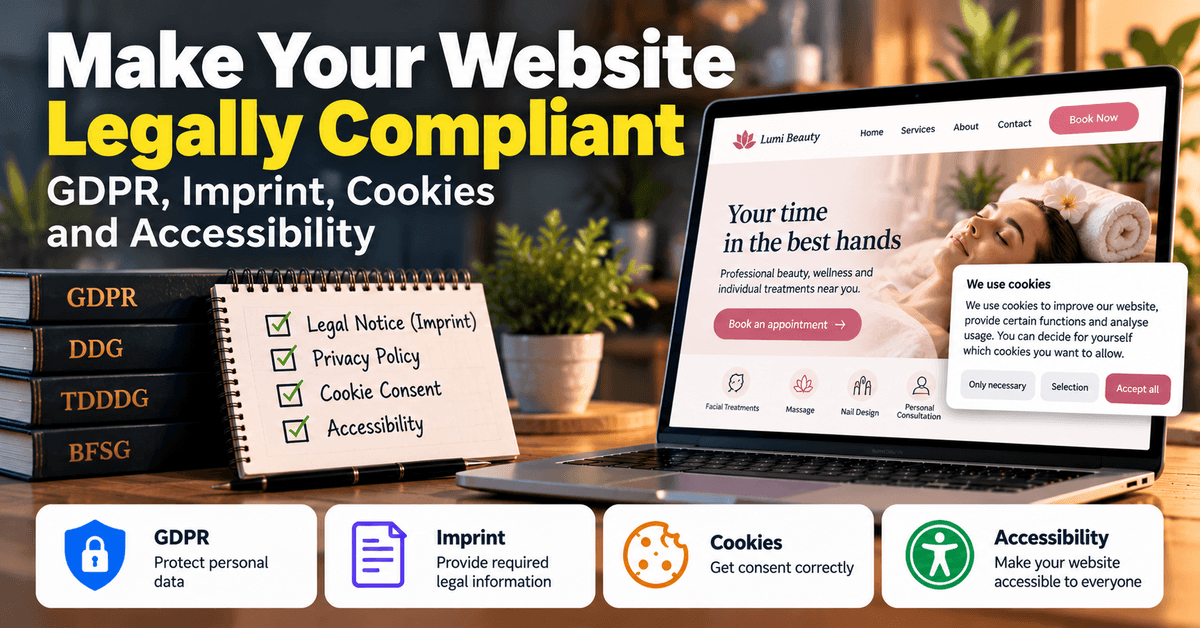
Note: This article offers general information and is not legal advice. What applies to your site depends on its technology, business model and company. Have legal statements reviewed by a qualified professional before publishing.
Key takeaways
- A business website in Germany generally needs an easy-to-reach legal notice (Impressum) and an understandable privacy policy.
- Whether cookie consent is required depends on which services the site actually loads, not on how the banner looks.
- First check which external services load, then decide about texts and consent.
Contents
A website should be more than attractive—it should be carefully configured
A business website does more than display design, text and contact details. It may process personal data, connect to external services or enable consumers to enter into contracts online. Before launch, operators should review which information and technical obligations apply to their specific website.
There is no single checklist that automatically fits every website. A basic information page, contact form, appointment-booking system and online shop can raise different questions. This guide is a structured starting point, not an individual legal assessment.
1. Impressum: identify the operator and provide contact information
Provider-identification duties may apply to commercial digital services. Section 5 of Germany’s Digital Services Act (DDG) is a key provision. Whether it applies and which details are required depend on the operator and the service. Additional rules may apply to particular professions or legal forms.
Depending on the case, provider information may include:
- the provider’s or company’s name and, where relevant, legal form;
- an address suitable for formal service;
- information enabling prompt electronic contact;
- register details if the provider is registered;
- supervisory or professional information where applicable;
- other legally required identification details where relevant.
This is not a universal list of mandatory fields for every website. Check the requirements for your legal form and activity. Older templates referring to the former TMG should be reviewed and updated where necessary.
Practical tip: Make the provider information easy to find and directly accessible, for example through a clearly labelled footer link. The exact presentation should meet the applicable rules.
2. Privacy notice: explain the data processing that actually occurs
Under the GDPR, controllers must provide transparent information to individuals in relevant circumstances. A website may process personal data through contact forms, appointment bookings, newsletters, server logs or analytics tools.
The privacy notice should be based on the actual processing activities. Review, in particular:
- who controls the processing and how to contact them;
- what data is processed and for what purposes;
- the legal basis relied on for each relevant activity;
- recipients or service providers that may receive data;
- retention periods or the criteria used to determine them;
- individuals’ rights and how to exercise them;
- transfers to countries outside the EEA and applicable safeguards.
A copied template can be incomplete or misleading if it does not match the services actually used. Adding a booking system, newsletter platform, analytics product or external embed may require the notice to be reviewed.
3. Cookies and similar technologies: assess them before deciding on consent
Section 25 of Germany’s TDDDG concerns storing information on, or accessing information from, users’ devices. Consent is generally required for activities that do not fall within a statutory exception. Related personal-data processing must also comply with the GDPR.
Not every cookie automatically requires consent, and not every website automatically needs a cookie banner. The purpose, technical necessity, implementation and relevant exceptions matter. The legal assessment cannot be made from a cookie’s name alone.
Check whether the website uses, for example:
- analytics or marketing technologies;
- advertising or retargeting pixels;
- maps, videos or other embeds that connect to external services on page load;
- features that store or access information on a device.
Where consent is required, the relevant technology should not be activated before valid consent. A banner is not enough if the technology is already running.
Also review whether the choice is understandable, refusal is not unnecessarily obstructed, and users can later change or withdraw their choice where required. The actual design and implementation should be checked against current rules.
4. Third-party services: review fonts, maps, videos and tracking
Third-party services may connect to external servers when a page loads and transmit data. Whether this is lawful and which safeguards are needed depend on the service, its configuration and the processing involved.
External fonts
When fonts are loaded from an external provider, the browser may send information—such as an IP address—to that provider. Hosting suitable font files locally can avoid the external request. It is not, by itself, proof of complete privacy compliance: other website components and licence terms still need review.
Maps, videos and other embeds
An embedded map or video may contact its provider as soon as the page loads. Depending on the service and setup, it may be appropriate or necessary to load the content only after a user action or consent. Assess the actual integration rather than relying only on a plugin’s marketing claims.
Technical review questions
- Which external services are contacted on the first page load?
- Do analytics or advertising scripts run before any required consent?
- Do embedded elements load automatically?
- Do the privacy notice and consent configuration reflect the services actually active?
A technical scan can identify clues, but it does not replace the legal assessment of each connection.
5. Accessibility: assess whether the BFSG applies
Germany’s Accessibility Strengthening Act (BFSG) has applied since 28 June 2025 to certain products and services. It covers, among other things, certain e-commerce services. Whether a specific online offer is covered depends on its function and the statutory definitions.
A purely informational or promotional page is not automatically equivalent to an online shop or booking flow through which consumers can conclude a covered contract. Assess the actual service.
The BFSG provides an exemption for microenterprises offering or providing services. The statutory definition depends, among other things, on employee numbers and financial thresholds. The conditions must be checked for the individual business; simply describing a company as “small” is not enough.
Regardless of legal applicability, accessible design can improve usability:
- sufficient colour contrast and readable text;
- keyboard operability;
- clear labels for forms and buttons;
- useful alternative text for informative images;
- visible, understandable error messages;
- a logical heading structure.
These are useful foundations, but they do not amount to a complete BFSG conformity assessment.
6. Common oversights on small-business websites
- Outdated provider information: An old template is reused without updating legal references or details.
- Privacy notice does not match actual practice: New services are added, but the notice remains unchanged.
- Consent is only visual: A banner appears while technologies requiring consent are already running.
- Third-party services are not inventoried: Maps, videos, fonts and marketing tools are embedded without review.
- Booking and checkout features are treated in isolation: They may introduce additional data processing and, depending on the service, other requirements.
- No review after changes: Plugins, tracking or booking services change without a fresh assessment.
7. Practical pre-launch checklist
- Is the provider information accurate, accessible and appropriate for this business?
- Does the privacy notice reflect the website’s actual features and services?
- Have contact forms, bookings, newsletters and other data flows been documented and reviewed?
- Have the cookies and similar technologies been identified, and has consent necessity been assessed?
- Are technologies requiring consent activated only after consent?
- Can users manage or withdraw consent where required?
- Have external fonts, maps, videos and tracking services been reviewed?
- Has the BFSG’s applicability or a relevant exemption been assessed for the actual offer?
- Is there a process to repeat the review when the website changes?
The order in which to check things
Starting with the cookie banner means starting at the wrong end. A sensible order:
- Inventory: Which services does your site load from outside (fonts, maps, videos, booking tool, statistics)? Your browser's developer tools show them under “Network”.
- Required pages: Are the legal notice and privacy policy one click away from the footer of every page, and up to date?
- Match the privacy text: Does the privacy policy name exactly the services from step 1, no more and no fewer?
- Decide on consent: Only technology that requires consent needs a prompt. Where possible, drop the service or host fonts locally.
- Check accessibility: Contrast, alt text for images, keyboard operation and understandable forms.
- Document it: Note when you checked what. Check again after every larger change.
Conclusion: treat website review as ongoing quality assurance
Before launch, businesses should review more than design, mobile layout and SEO. They should map personal-data processing, identify third-party services, test consent controls and determine whether specific requirements—such as accessibility rules—apply to their online offer.
A useful first step is to inventory all website features. Then review provider information and privacy notices, technically test consent, and assess BFSG applicability. Seek qualified advice where legal questions remain.
Disclaimer: This article is general information, not legal advice. It does not certify that any particular website is legally compliant or meets BFSG requirements.
Official sources for further review
Frequently asked questions
Does every website in Germany need an Impressum?
Provider-identification duties may apply to commercial digital services. Whether they apply and what details are required depend on the operator and service. Check the relevant legislation and any sector-specific requirements.
Does every website need a cookie banner?
No, not automatically. First identify the cookies and similar technologies in use and assess whether consent is required. Privacy information may still be necessary without a banner.
Does self-hosting Google Fonts automatically make a website GDPR-compliant?
No. Local hosting can avoid an external font request, but it is only one technical consideration. Other processing activities and licence terms still need review.
Does the BFSG apply to a small studio with online appointment booking?
There is no blanket answer. The booking and contract functionality, the law’s scope and possible exemptions—including the microenterprise exemption—matter. Have the actual offer assessed.